As AI agents become more advanced, the biggest challenge isn't just making them smarter or faster. It's about keeping their actions contained. When an AI agent can execute code, install packages, or interact with infrastructure, the real question shifts from can it reason to what happens when it reasons incorrectly.
This is where the concept of containment becomes critical. Enterprises are quickly learning that as agents gain more autonomy, the risks grow. In this post, we'll explore why sandboxes are essential for AI agents, how they work, and what developers need to know to keep their systems safe.
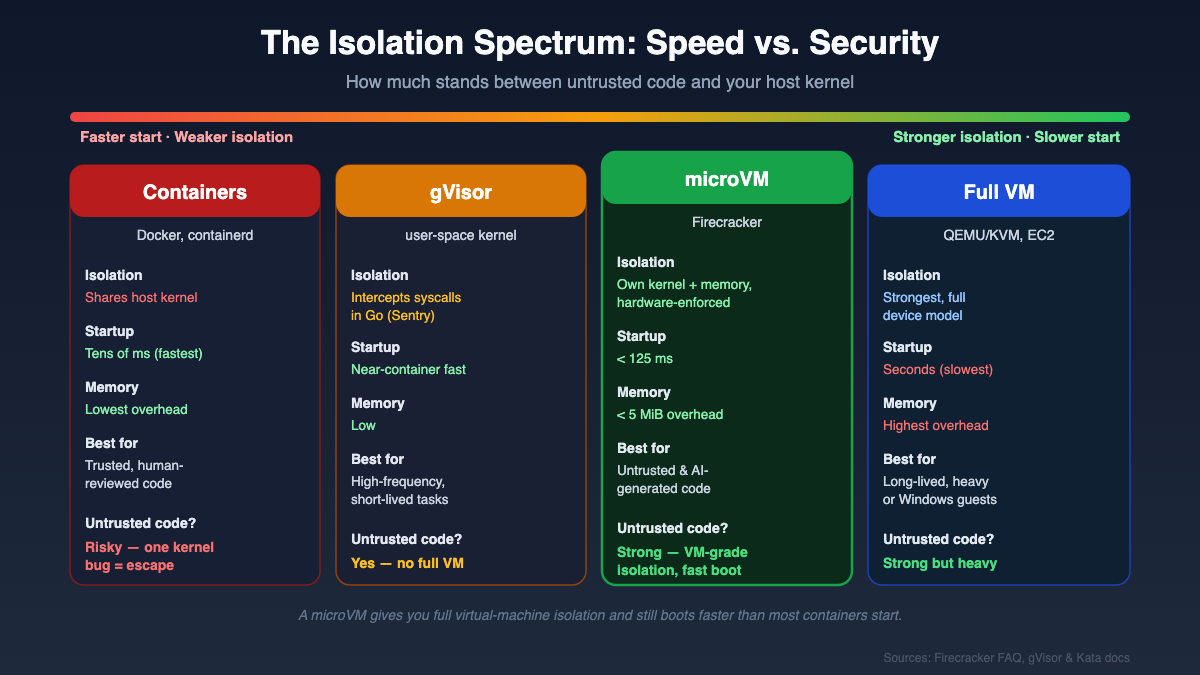
A sandbox, in the context of AI and software, is a secure, isolated, and controlled environment. It allows code to run and experiments to happen without risking the safety of the broader system. Think of it as a locked room. Whatever happens inside, stays inside. This means any mistakes, bugs, or even malicious actions are contained and can't affect the rest of your infrastructure. For AI agents, especially those generating and executing code, sandboxes are not just helpful, they're essential for safe experimentation and operation.
Risk-averse organizations have refused to run untrusted or third-party code, plugins, and dependencies without proper vetting on systems they care about for as long as those systems have existed. The pattern you see again and again in organizations that take risk seriously is simple: isolate first, observe, then trust. What changed is the volume. Agentic development and vibe coding mean far more untrusted, machine-generated code is executing near things that matter, and it is happening at machine speed.