Databricks Genie Agents: Setup, Testing & Governance

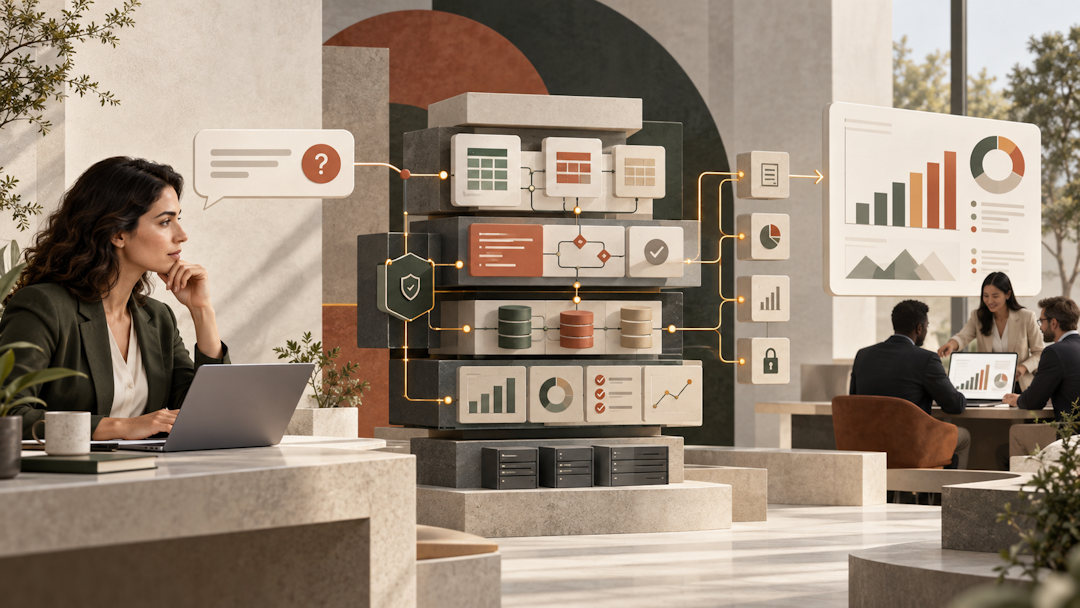
Databricks Genie Agents - Setup Testing and Governance

What happens when business users can ask enterprise data a question in plain English, without waiting for an analyst to write the SQL?   That promise sounds simple and Databricks’s Genie One amd the Genie Agents are geared towards making this happen. In this post, I am going to discuss how to make that happen … Read more

Databricks Genie One vs Genie Code vs Genie Agents

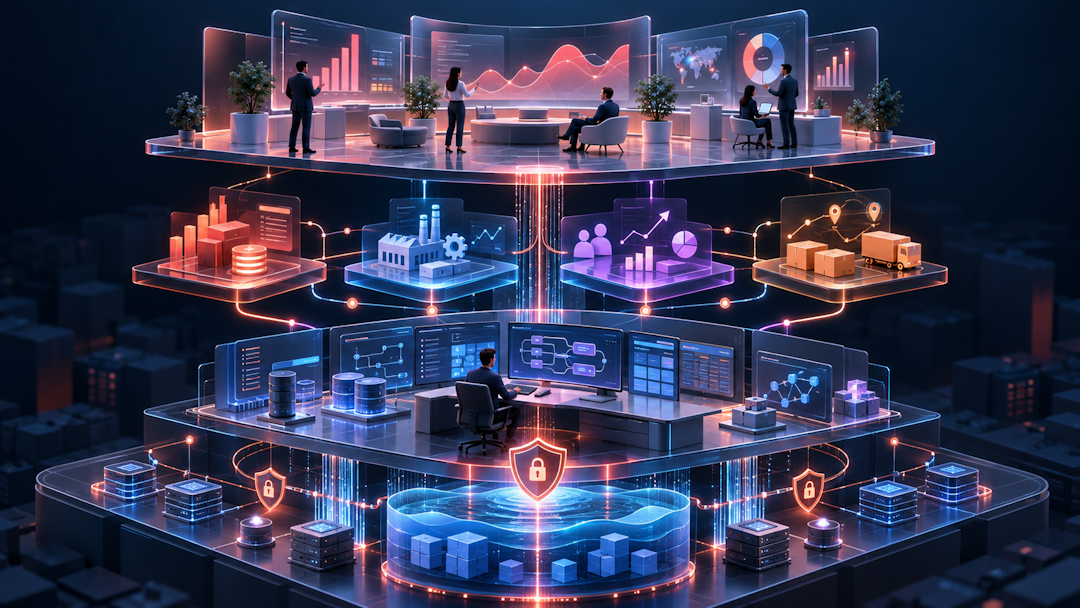
Databricks Genie One vs Genie Code vs Genie Agents

I have been fascinated by the improvements Databricks keeps making in their Genie offering and I have a habit of sharing what I practice. So, this post is dedicated to Genie AI and different features within it. So, let’s get into it. Speaking of Genie, Databricks has put the Genie name on three experiences, and … Read more

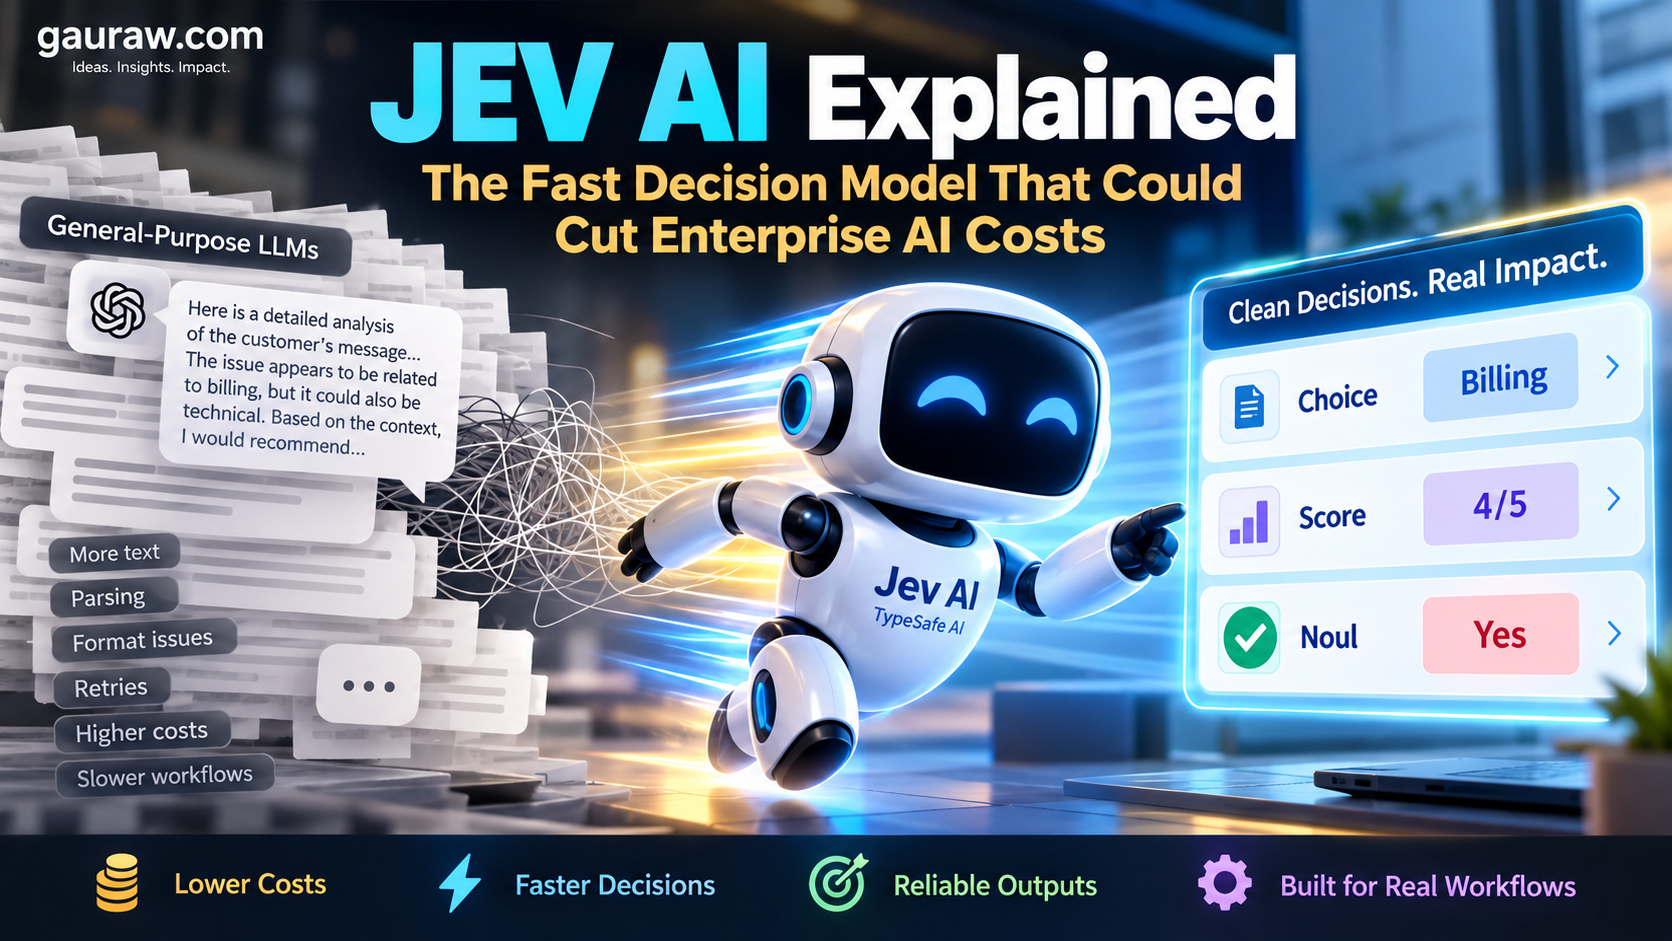
JEV AI Explained: The Fast Decision Model That Could Cut Enterprise AI Costs

JEV_AI_EXPLAINED_ENTERPRIZE_DECISION_AI_VS_GENERAL_PURPOSE_FRONTIER_LLMs

So far, regardless of the kind of work with AI we do, most of us deal with Large Language Models that generate text responses that humans understand clearly and incidentally, AI models are also able to understand it. But more often we deal with situations where we get a paragraph in response when the software … Read more

Sandboxing Third Party Plugins, Tools, Untrusted and AI-Generated Code: An Enterprise Guide

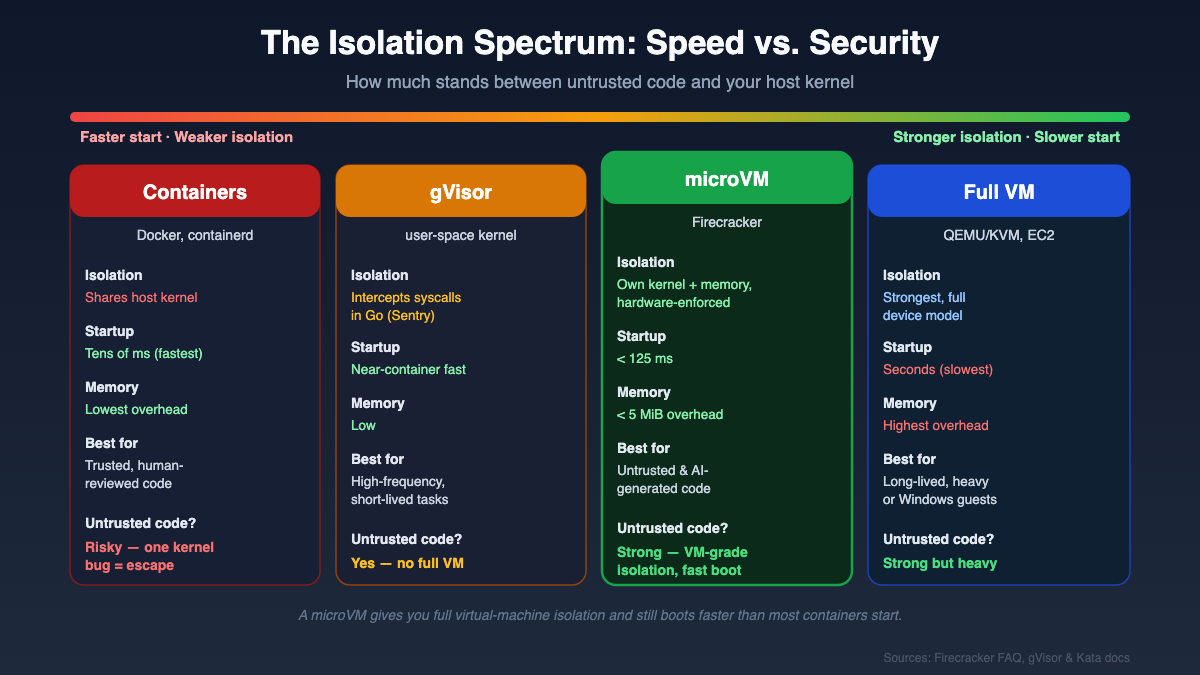
Comparison of container, gVisor user-space kernel, Firecracker microVM, and full VM isolation models across security and startup speed.

As AI agents become more advanced, the biggest challenge isn't just making them smarter or faster. It's about keeping their actions contained. When an AI agent can execute code, install packages, or interact with infrastructure, the real question shifts from can it reason to what happens when it reasons incorrectly.

This is where the concept of containment becomes critical. Enterprises are quickly learning that as agents gain more autonomy, the risks grow. In this post, we'll explore why sandboxes are essential for AI agents, how they work, and what developers need to know to keep their systems safe.

A sandbox, in the context of AI and software, is a secure, isolated, and controlled environment. It allows code to run and experiments to happen without risking the safety of the broader system. Think of it as a locked room. Whatever happens inside, stays inside. This means any mistakes, bugs, or even malicious actions are contained and can't affect the rest of your infrastructure. For AI agents, especially those generating and executing code, sandboxes are not just helpful, they're essential for safe experimentation and operation.

Risk-averse organizations have refused to run untrusted or third-party code, plugins, and dependencies without proper vetting on systems they care about for as long as those systems have existed. The pattern you see again and again in organizations that take risk seriously is simple: isolate first, observe, then trust. What changed is the volume. Agentic development and vibe coding mean far more untrusted, machine-generated code is executing near things that matter, and it is happening at machine speed.
Read more

Spec-Driven Development with GitHub Spec Kit: An Enterprise & Agile Guide

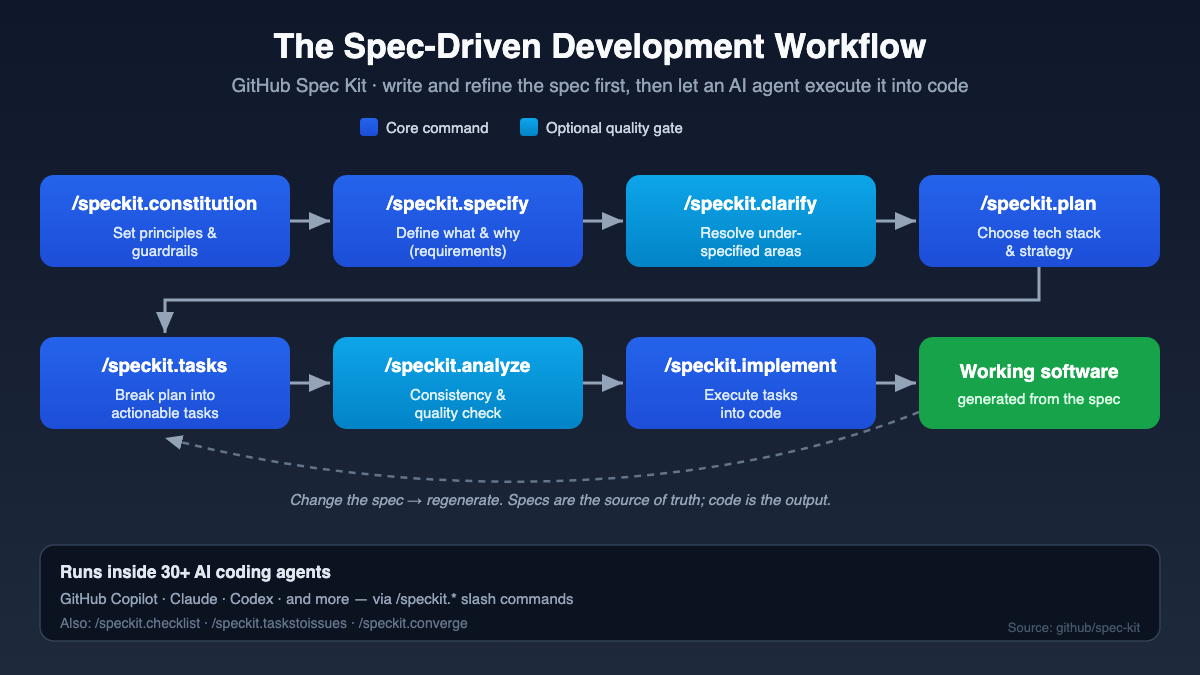
Diagram of the GitHub Spec Kit spec-driven development command workflow, from constitution through implement to working software.

What GitHub Spec Kit is, how its /speckit command workflow scaffolds spec-driven development, and why writing the spec first then letting AI agents build it fits enterprise, multi-developer, agile teams.

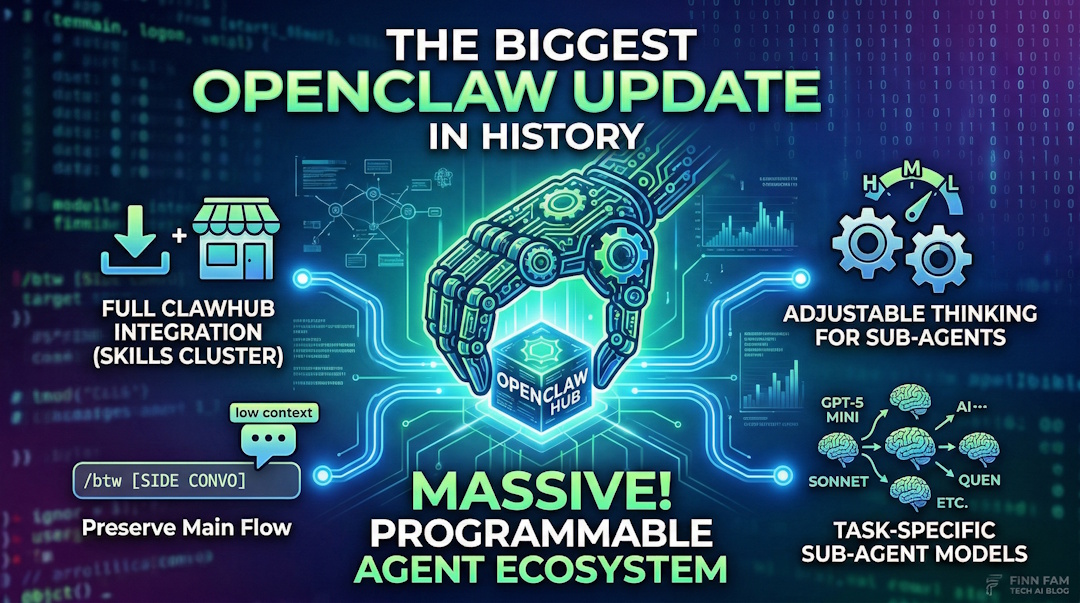
The Biggest OpenClaw Update Just Dropped. Here Is Everything You Need to Know (March 2026)

OpenClaw Update - March-2026- Massive-Update Ecosystem

OpenClaw v2026.3.22 just dropped with ClawHub marketplace integration, the /btw side conversation command, adjustable sub-agent thinking, multi-model sub-agents, and critical session management fixes. Here is what changed and what you need to do about it.